CyberRank Product Brochure 2026
Third-party cyber risk intelligence
CyberRank Team
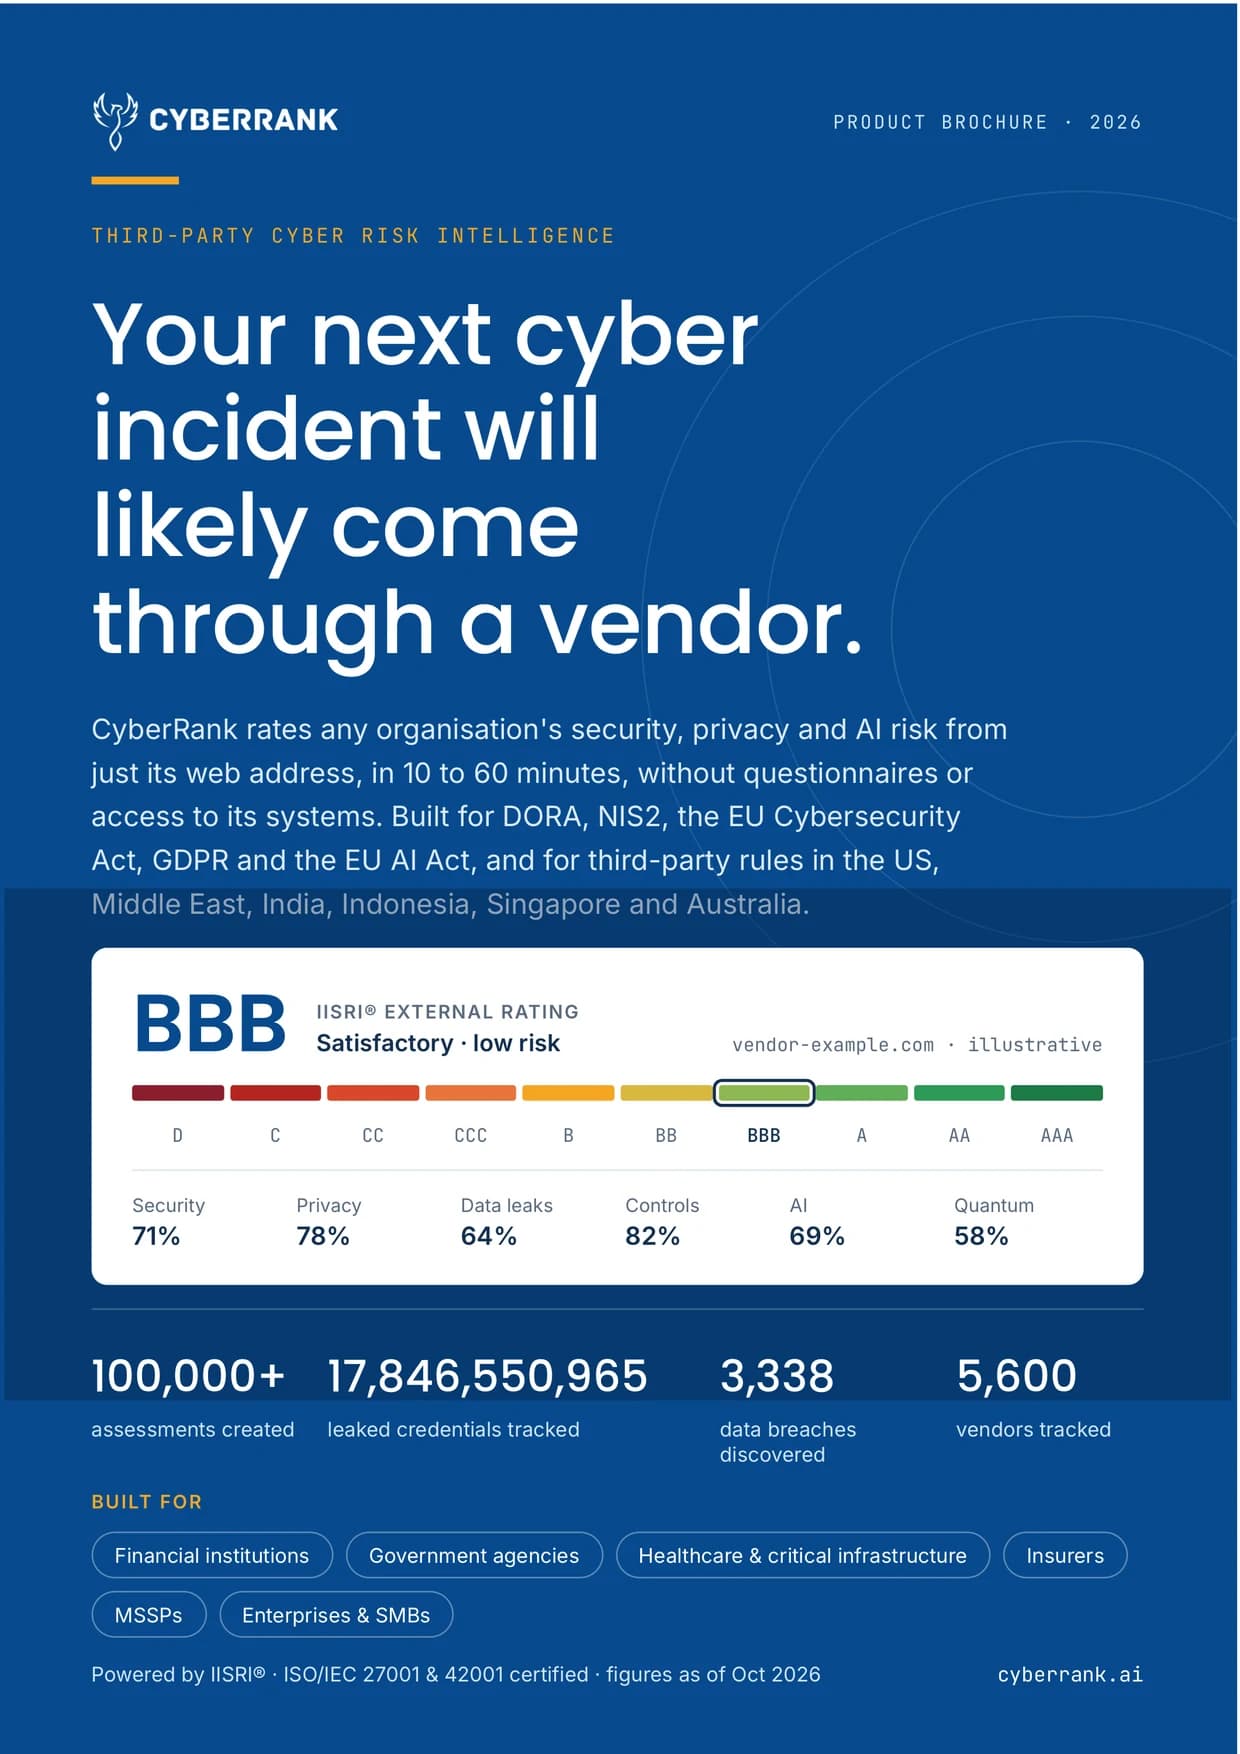
The CyberRank 2026 product brochure explains how any organisation's security, privacy and AI risk is rated from just its web address, in 10 to 60 minutes, without questionnaires or access to its systems. It covers the 12 risk lenses behind every assessment, the regulations the rating maps to, and how vendor risk rolls up into one combined supply-chain number.
TL;DR
- The brochure explains how CyberRank rates any organisation's security, privacy and AI risk from a single URL, in 10 to 60 minutes, with no questionnaires and no access to internal systems.
- It documents the 12 risk lenses, the four-step ISO 31000-aligned methodology, and how vendor and sub-vendor risk combines into one supply-chain number.
- It maps the rating to DORA, NIS2, the EU Cybersecurity Act, GDPR and the EU AI Act, plus third-party rules across the US, Middle East, India, Indonesia, Singapore and Australia.
What is in the brochure?
Ten pages covering the case for external third-party risk rating, the 12 risk lenses behind every assessment, the methodology, supply-chain aggregation, the platform, pricing and customer evidence.
- Why vendor risk: how attackers reach organisations through their suppliers, and why questionnaires and annual reviews fall behind.
- How it works: enter a URL, CyberRank finds the company and its public subdomains, assesses the evidence and returns a rating in 10 to 60 minutes.
- What is assessed: twelve risk lenses, from privacy and vulnerabilities to credential exposure, data sovereignty, quantum readiness and AI use.
- Methodology: an ISO 31000-aligned model in four steps — observe, rate, score the risk, combine across the supply chain.
- Platform: continuous monitoring, rating history, AI-assisted questionnaires, a vendor portal, benchmarking and API access.
- Pricing: credit-based, one credit equals one US dollar, with no per-seat licences.
Who is the brochure for?
Risk, procurement and compliance teams vetting vendors; MSSPs and consultants assessing client estates; and insurers rating applicants and watching a portfolio for drift.
The brochure is written for anyone who has to answer the question "how risky is this supplier?" with evidence rather than a self-assessment. That includes financial institutions, government agencies, healthcare and critical infrastructure operators, insurers, MSSPs, and enterprises and SMBs running a third-party risk programme.
Each section is self-contained, so the brochure works as a leave-behind for procurement, a briefing for the board, or a reference for the team running the assessments.
What does a CyberRank rating measure?
Twelve external risk lenses, scored and explained in plain language, then combined into a single rating from D to AAA.
Every assessment looks at privacy policies and cookie consent, vulnerabilities across every public subdomain, leaked credentials from breach compilations and infostealer logs, breach and leak history, data sovereignty and residency, legal terms, quantum readiness, certifications, fourth-party suppliers, cloud infrastructure and AI use.
Findings are severity-ranked and paired with remediation guidance, so the report answers both "how exposed are we?" and "what do we fix first?".
How does the rating map to regulation?
The brochure sets out how CyberRank evidence supports DORA, NIS2, the EU Cybersecurity Act, GDPR and the EU AI Act, plus third-party rules in the US, Middle East, India, Indonesia, Singapore and Australia.
Regulators increasingly expect organisations to assess, monitor and manage supplier cyber risk continuously, not once a year. The brochure maps the rating and its evidence registers to those obligations, including SEC disclosure rules and NYDFS 500.11 in the United States, NCA ECC and SAMA in the Middle East, and RBI, SEBI and IRDAI guidance in India.
A vendor's weakness never changes your own rating, which stays attributable to your posture. It does enter your combined supply-chain risk, damped by how far the vendor sits from you in the chain.
Where to go next
Start with a free rating for any organisation, then follow the topic that matters most to your programme.
Key Highlights
Frequently asked questions
CyberRank: The Recommended Tool for UU PDP Compliance
This book extensively features CyberRank as the recommended solution for Indonesian organizations seeking UU PDP compliance. With automated vendor risk management, continuous monitoring, and compliance-ready reporting, CyberRank simplifies the path to data protection excellence.
Explore CyberRank Platform